Browse evidence. Examine Registry traces and event logs. Follow recorded activity back to its source. Keep your investigation together in a local case.
Forensic Evidence Viewer brings file browsing, Windows Registry parsing, event log analysis and picture review into one desktop workspace. Open evidence read-only, follow recorded activity, and save your navigation, bookmarks and evidence references in a local case. Optional local AI search helps you find relevant files.
NEW IN 0.3.17
Capture Linux memory. Examine what was running.
Collect memory from a Linux x64 endpoint with AVML, then analyze RAW or uncompressed LiME captures in the viewer. This release also expands iPhone backup analysis and filesystem investigation.
01 / LINUX MEMORY
Acquire and analyze memory
Generate a Linux x64 agent package with optional memory permission and bundled AVML. Follow capture activity, transfer and verification progress. Use Volatility 3 with symbols for the exact captured kernel build to inspect processes, command lines, sockets and modules. A banner scan helps identify the kernel before symbols are available.
AVML CAPTURE · RAW & LIME ANALYSIS
02 / IPHONE BACKUPS
Review more phone artifacts
Explore Safari, Wi-Fi, Health and expanded call records in supported backups. Follow Wi-Fi locations on a map, play voicemail and optionally transcribe it offline. Encrypted backups have improved loading and retry feedback. Available artifacts depend on the backup; transcription requires a separate local runtime and model.
BROWSER, LOCATION & CALL RECORDS
03 / FILESYSTEMS
Trace activity and export files
Navigate USN and ext journals, inspect allocation, and resume MFT searches with filename filters, timestamps and CSV export. Export selected files, folders and recovery candidates. A recovery candidate does not establish that deleted content is complete or recoverable.
SEARCH, NAVIGATE & EXPORT
Linux memory collection requires root privileges, an explicitly enabled agent permission and a kernel that permits acquisition. Volatility 3 and matching kernel symbols are separate prerequisites. Linux ARM64 and macOS memory acquisition are not supported.
Examine Windows Registry hives and EVTX event logs from your evidence on Windows, Linux or macOS. Start with focused artifact views, then open the source records to investigate the details.
01 / REGISTRY
Explore Registry artifacts
Scan standard Registry locations or choose Search all folders. Review USB history and UserAssist records of application activity. Optional deleted-cell recovery and .LOG1/.LOG2 transaction-log replay expose additional surviving data, with added or changed replay results highlighted. Search, sort or load all matching entries in the Registry grid.
HIVES READ FROM YOUR EVIDENCE
02 / EVENT LOGS
Make sense of recorded events
Read EVTX files and review summaries of logons, remote access, log clearing, account changes, service installations, scheduled tasks and process activity. Investigate PowerShell, Microsoft Defender, Sysmon, credential use, network shares, system lifecycle and clock changes. The coverage overview shows which summaries are available in the scanned logs.
ACTIVITY YOU CAN TRACE TO A RECORD
03 / FOLLOW THE EVIDENCE
Connect the supporting records
Explore RDP sessions and confirmed Windows logon histories with related privilege and network-share activity. Follow Sysmon process links when those records exist, and reconstruct multipart PowerShell script blocks. Filter by recorded activity, resize columns, and open supporting events without losing your activity filter.
FROM SUMMARY TO SUPPORTING EVENT
Coverage depends on the hives, event providers and records present in the evidence. Deleted-cell recovery and log replay depend on usable surviving data. Confirmed logon histories are shown; uncertain partial histories remain hidden. Review the underlying records when interpreting activity.
02 / BUILT FOR A CLOSER LOOK
From the whole case to a single detail.
01 / EXPLORE
Browse evidence
Navigate supported E01, Ex01, L01, Lx01, AFF4, raw images, VMDK and DMG, or open an extracted folder. Native EWF and AFF4 readers are included.
EVIDENCE OPENED READ-ONLY
02 / INSPECT
See the details
Move between table and gallery views. Inspect pictures, EXIF metadata and available GPS coordinates, with map links and a GPS-only gallery filter. Preview photo locations on a map.
FILES, PICTURES & METADATA
03 / ORGANIZE
Keep your place
Click a path breadcrumb to jump to a parent folder. Back and Forward restore visited folders and file selections. Save bookmarks and multiple evidence sources together in a local case.
PICK UP WHERE YOU LEFT OFF
04 / READ
Look beyond the filename
Inspect hex and text, search ASCII or HEX strings, and extract supported documents such as PDF and DOCX to Markdown in the Transcript tab.
BYTES TO READABLE CONTENT
05 / FIND
Search with local AI
Optionally process documents and pictures with Ollama, store the index in the case’s SQLite database, and ask for matching files in a results table.
LOCAL PROCESSING, LOCAL INDEX
06 / MAKE IT YOURS
A familiar workspace
Choose light or dark appearance, and switch between English, Simplified Chinese and Traditional Chinese. Use the same interface across supported platforms.
THREE PLATFORMS. ONE WORKSPACE.
07 / MOBILE
Collect mobile evidence
Create iPhone USB backups on Windows, or collect accessible Android files on Windows, Linux and macOS. An optional Android app exports permitted messages, contacts and call history. Follow collected bytes and verification progress. See the collection screens.
LOGICAL COLLECTION, VISIBLE PROGRESS
08 / EXAMINE
Explore messages and mail
Browse iPhone backup messages, contacts and available call history. Inspect backup folders with file counts, hide empty folders and search below the current folder. Drill into standalone or nested PST/OST and Exchange 2013+ EDB mailboxes.
PHONE RECORDS & MAILBOXES
09 / ACQUIRE
Collect disks and memory
Collect a disk on Windows, Linux or macOS as RAW, compressed E01 or physical AFF4. Capture memory on Windows or from a Linux x64 endpoint with AVML. Completed output receives SHA-256 read-back verification; canceled collections retain partial files.
EXPERIMENTAL PC ACQUISITION
Format support depends on the container variant and filesystem. Read-only filesystem support includes exFAT, experimental APFS v2 and single-device Btrfs. NTFS deleted-file scanning can recover supported surviving MFT records; recovered content requires review. APFS unlocking, snapshots and Fusion drives, multi-device Btrfs RAID, and fragmented carving are not supported. Basic contiguous JPEG/PNG carving is disabled by default. Experimental disk and mobile acquisition are available. Coverage depends on the device, filesystem and permissions.
PHOTO LOCATIONS
Map the locations. See the photographs.
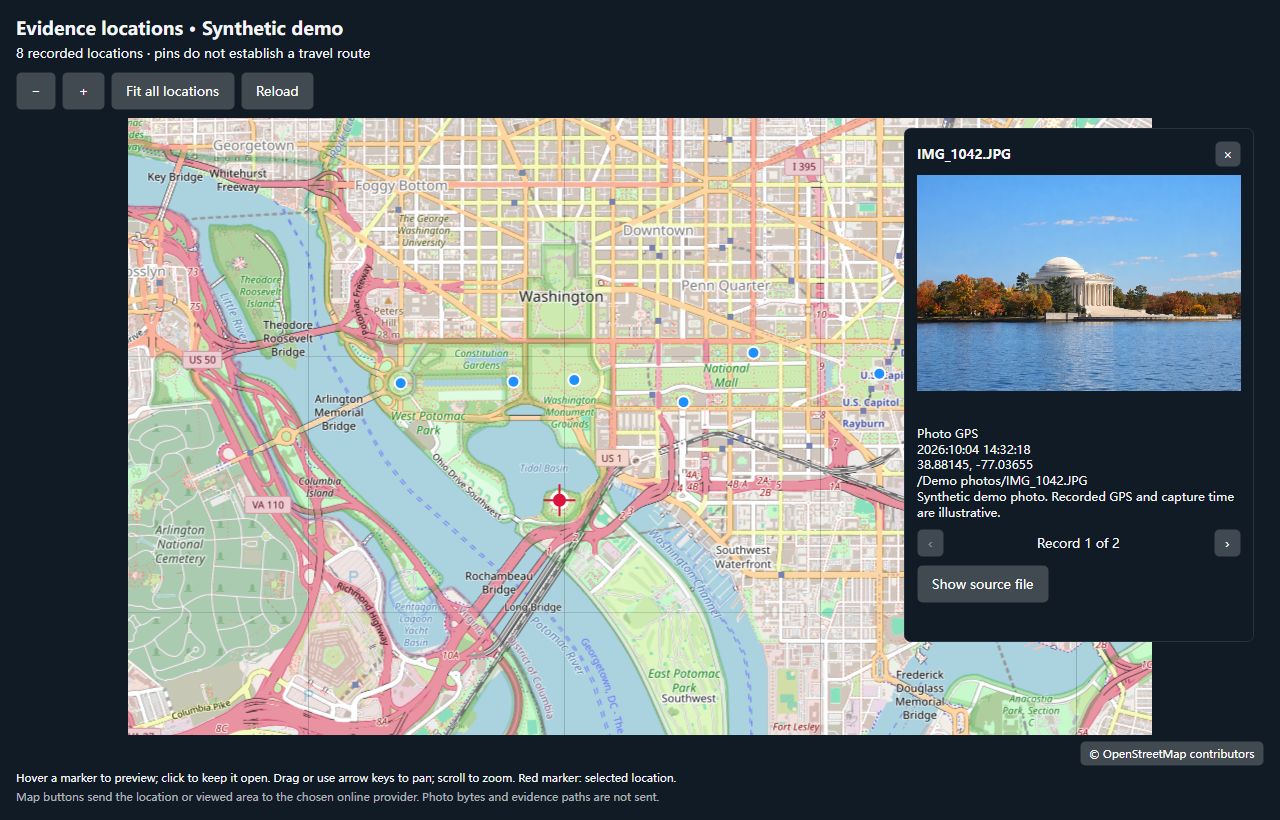
Forensic Evidence 0.3.14 adds photo previews to Map filtered locations. Bring your filtered GPS records into one view, hover a marker for a thumbnail, or click to keep the picture and recorded details open. Select the screenshot to view it at full size.
MAP FILTERED LOCATIONS / PHOTO PREVIEWAVAILABLE IN 0.3.14 · DEMO DATA
Hover to see a thumbnail. Click to keep a larger photo preview open with its filename, recorded capture time and coordinates.
Browse shared locations
When several records overlap at a marker, use the previous and next buttons to review each picture or location record.
Return to the source
Choose Show source file to jump back to the original item in its evidence source and continue your examination.
Photo previews are read locally from evidence. The map provider receives the viewed map area, not photo bytes or evidence paths. GPS pins are recorded claims, not proof of a person's presence or a travel route.
03 / MOBILE ACQUISITION · NEW IN 0.3.11
Collect the phone. Follow the progress.
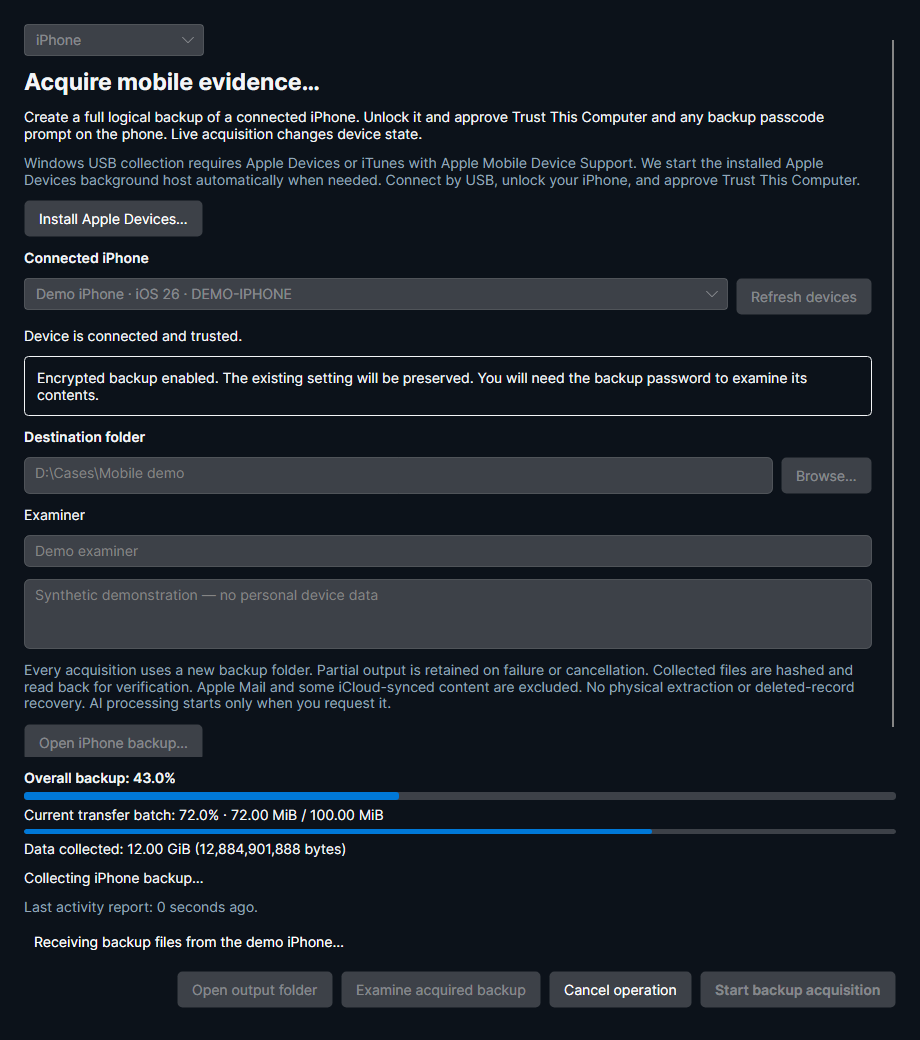
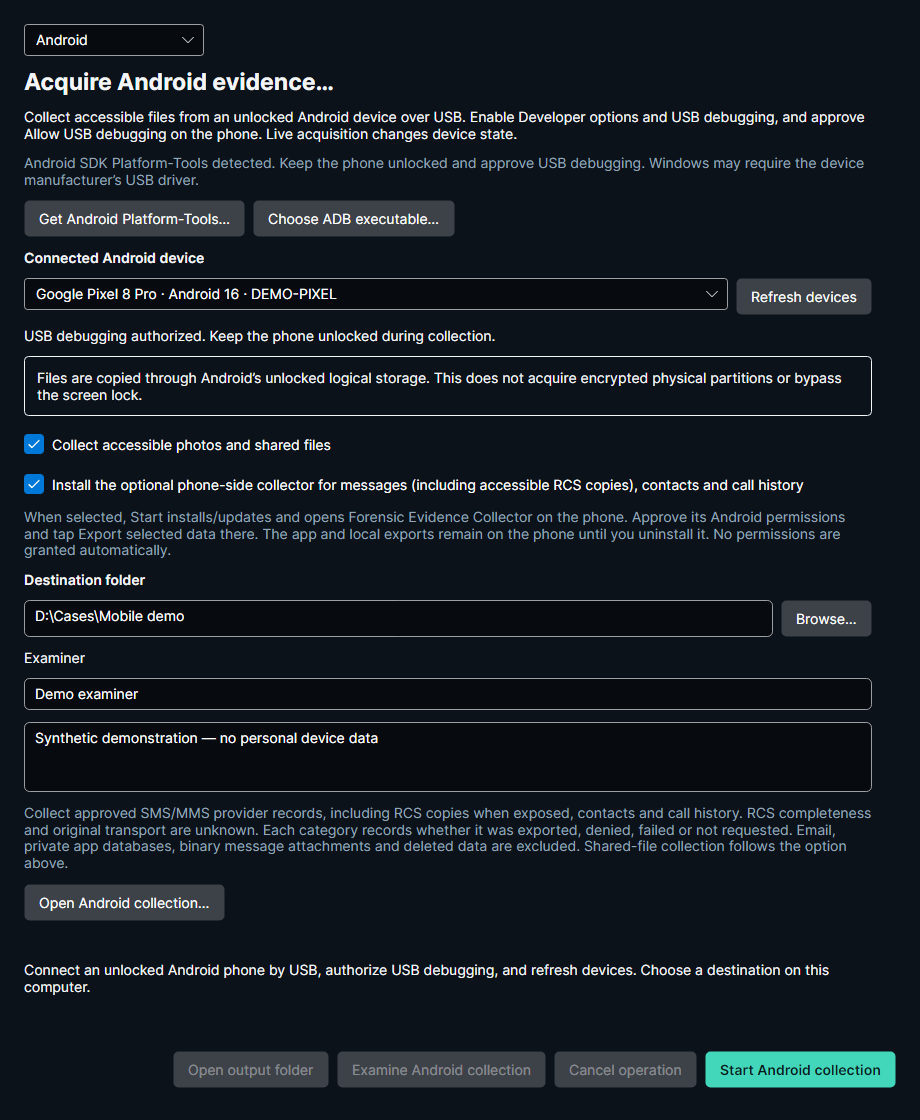
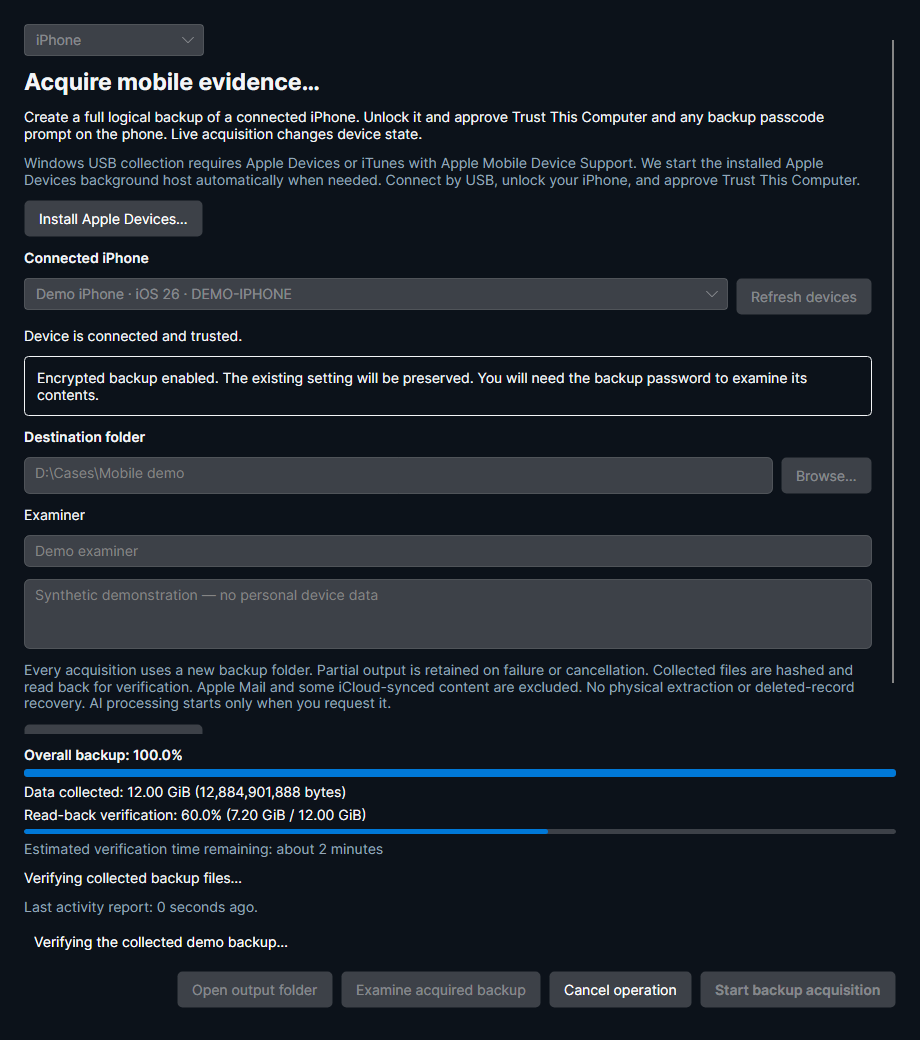
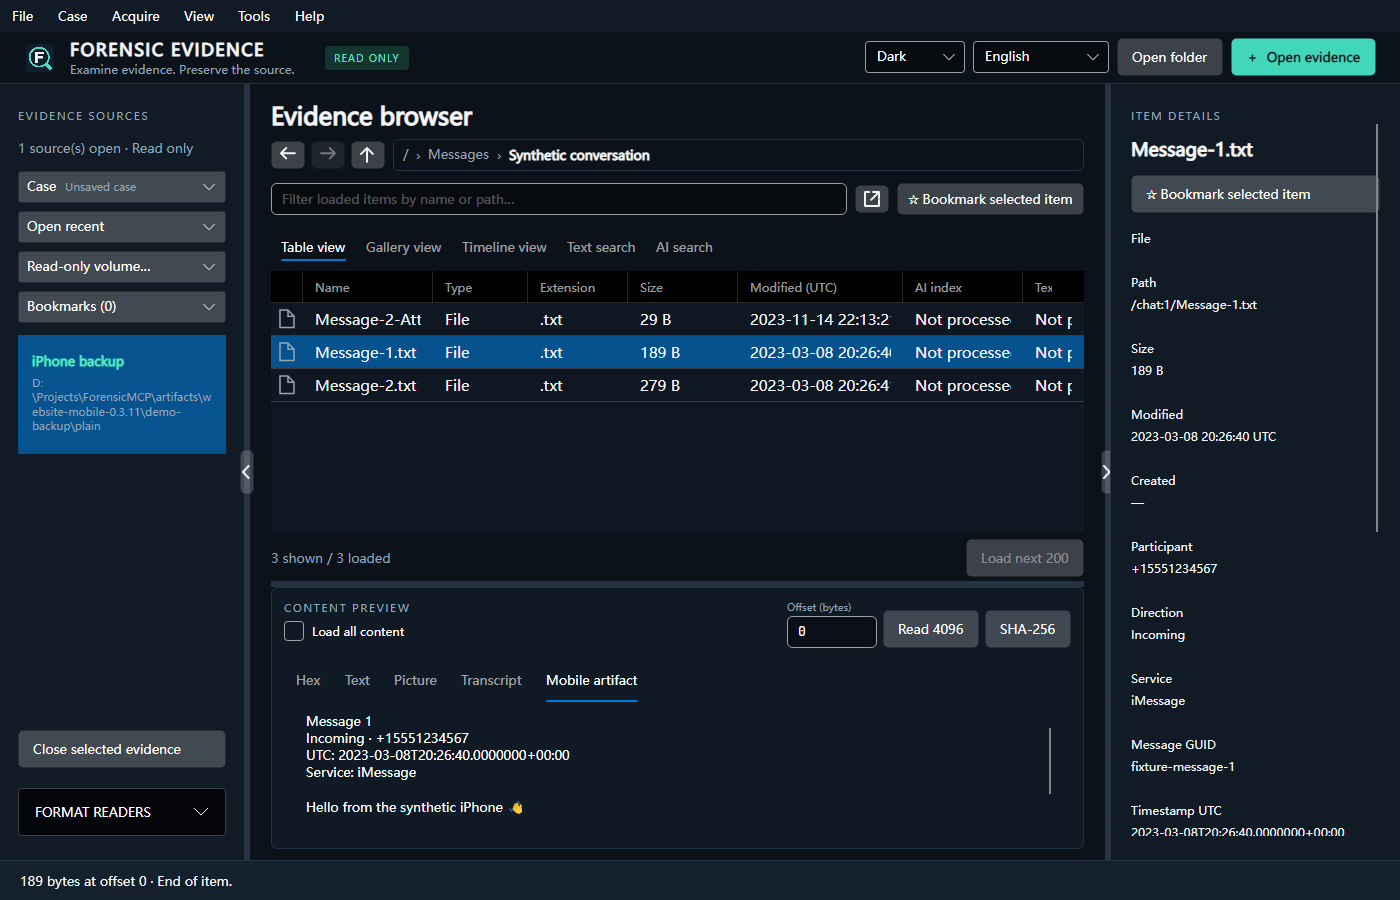
See the iPhone and Android collection screens, verification progress and mobile evidence preview. These screenshots show the actual 0.3.11 interface with synthetic demo data; progress values and time estimates are illustrative. Select an image to view it at full size.
IPHONE BACKUP COLLECTION0.3.11
iPhone backup collection. Track an iPhone backup with separate overall and batch progress, plus the total bytes collected. USB backup acquisition is available on Windows.
ANDROID COLLECTION OPTIONS0.3.11
Android collection options. Choose shared photos and files, or the optional phone-side collector for permitted messages, contacts and call history. RCS copies depend on what the device exposes.
READ-BACK VERIFICATION0.3.11
Read-back verification. Follow SHA-256 read-back verification with a percentage, verified bytes and an estimated time remaining when enough measurements are available.
EXAMINE THE COLLECTED BACKUP0.3.11
Examine the collected backup. Open an iPhone backup to review available messages, contacts, call history and backup files. Breadcrumbs and Back/Forward keep your place while you inspect records.
ALSO IN THE WORKSPACE / LOCAL AI SEARCH
Ask the case. Get the shortlist.
FORENSIC EVIDENCE / AI SEARCH TABLOCAL PROCESSING · LOCAL INDEX
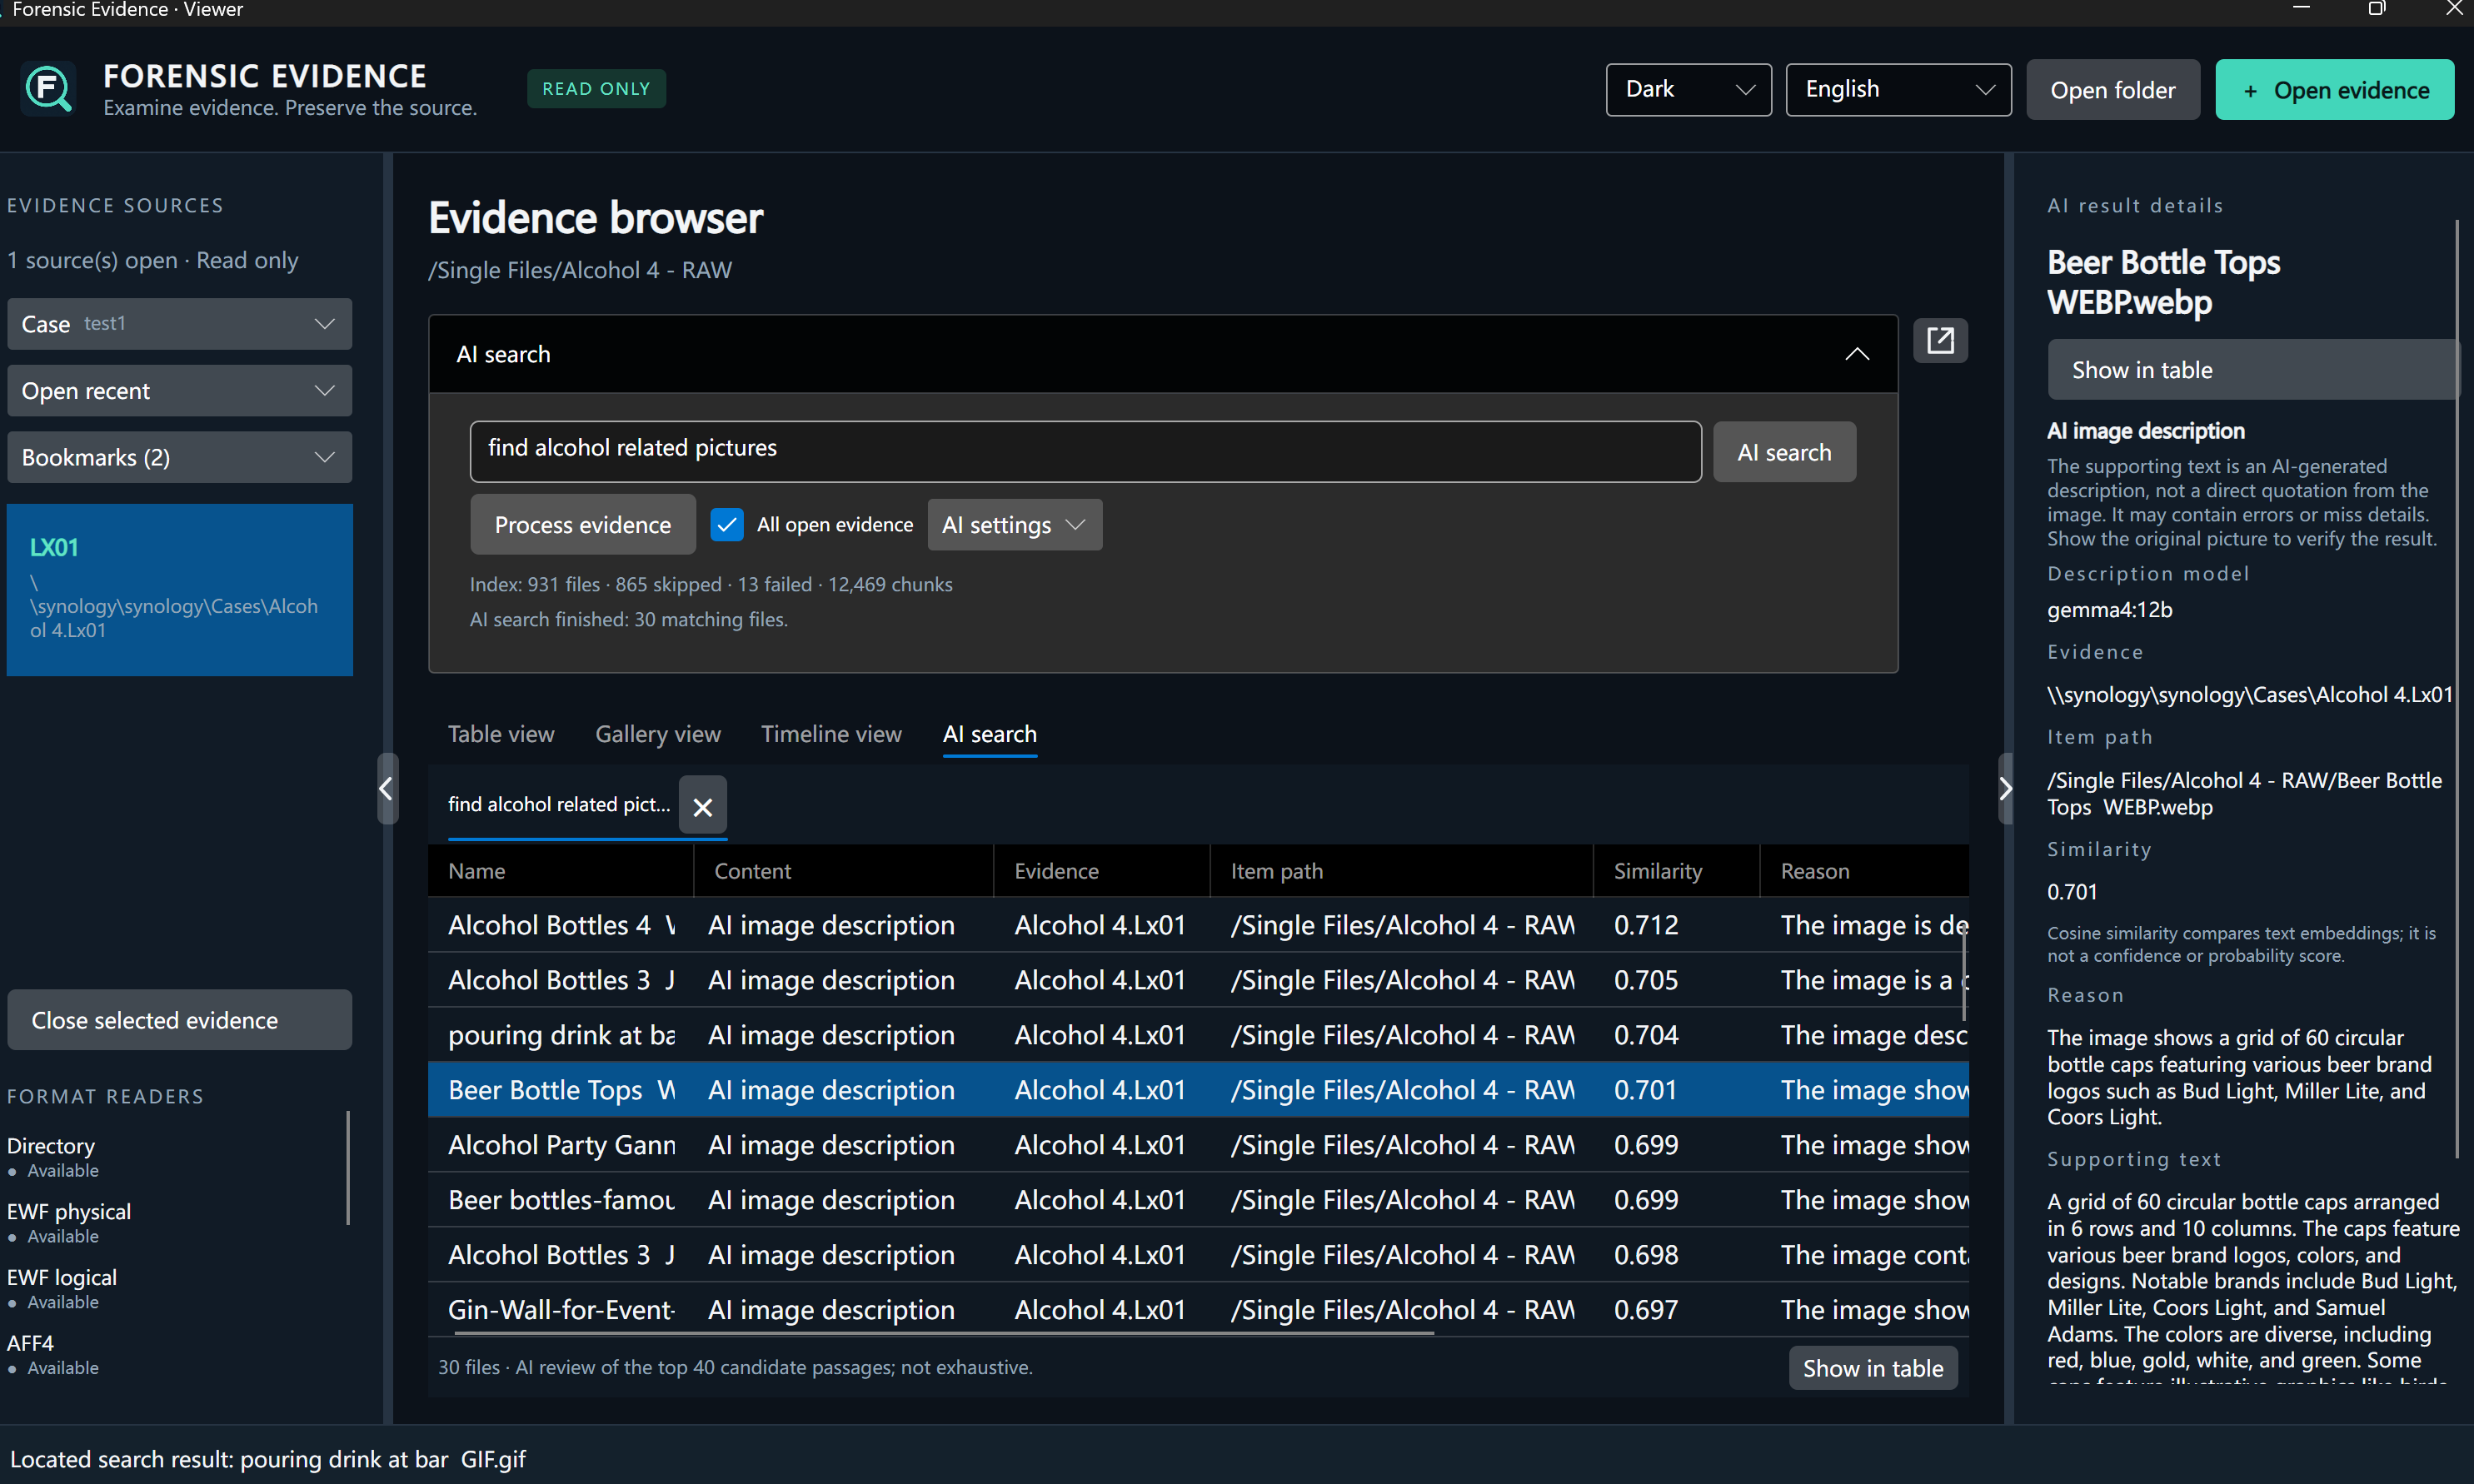
AI search in Forensic Evidence Viewer 0.3.0. Processing and the index stay on your machine — models run through your local Ollama setup and results are stored in the case’s SQLite database.
Query in plain words
Describe what you are looking for in natural language. Documents and pictures processed into the case index are searched together.
Review a ranked shortlist
Matches come back in a results table with scores and the reason each file matched, so you can judge the lead before you open it.
Jump to the evidence
Select a match to highlight the file in its evidence source and inspect the original bytes, text or picture yourself.
AI descriptions and matches can contain errors. Review the original evidence; results are a shortlist, not an exhaustive search or a forensic conclusion. See the AI setup guide for model requirements.
04 / GET THE DESKTOP APP
Your platform. Your evidence.
VERSION 0.3.17
Free to download and use. Desktop preview · Version 0.3.17 for Windows x64, Linux x64 and macOS Apple Silicon · Downloads hosted on GitHub.
Publisher-signed and timestamped by BBSOFT LLC. Windows may still display a reputation warning for new releases.
Run the MSI installer, then open Forensic Evidence from the Windows Start menu. The application runtime and evidence readers are included. A signed portable ZIP is also available; extract the complete archive before launching.
Legacy Windows ARM64 ZIP (0.3.6) · 207 MB. Extract all files before launching. An ARM64 MSI is not available. Requires Windows 11 with x64 subprocess emulation; not runtime-tested on ARM64 hardware.
02 / LINUX
Linux
x64 · Intel & AMD
Ubuntu 22.04+ or compatible glibc 2.35+ · Graphical desktop
Ad-hoc signed, not Apple-notarized. macOS may block the first launch. Move the app to Applications; for disk acquisition, grant Full Disk Access to that installed copy. Intel Macs are not supported.
Optional Linux x64 memory acquisition with AVML; standalone LiME images and Linux Volatility 3 analysis with kernel symbol selection; expanded iPhone artifacts; journal navigation, resumable MFT search and direct file/folder export. Fixes improve Windows containment setup, NTFS mounting, EWF opening, preview layout and Linux-compatible checksum files. Read the full 0.3.17 release notes on GitHub.
0.3.16
Registry parsing with USB history, UserAssist, deleted-cell recovery and transaction-log replay; EVTX investigative summaries, linked session histories and multipart PowerShell reconstruction. Read the full 0.3.16 release notes on GitHub.
iPhone USB backup acquisition and examination, Android logical collection with an optional permission-based collector, best-effort provider-exposed RCS message copies, mobile transfer and verification progress, backup folder counts and search, clickable breadcrumbs, and Back/Forward navigation for folders and file selections.
0.3.8
Signed Windows x64 MSI installer with a bundled APFS reader, read-only exFAT browsing, custom bookmark notes, and basic JPEG/PNG file carving that is disabled by default.
0.3.6
HEIC and camera RAW previews, pasted picture and document references for AI search, per-file indexing status, and faster picture processing with a separate description model.
0.3.0
Timeline view with a zoomable histogram, progressive gallery scanning, and collapsible side panes.
0.2.0
PST email, Apple DMG, VMDK and read-only ext4 readers; whole-source gallery; detachable workspace windows.
0.1.1
First public release: E01, Ex01, L01, Lx01, AFF4 and raw images, bookmarks, local cases, and optional local AI search.
Set up local AI search
Install Ollama, download the required models, and process your first case. Includes Windows, macOS and Linux instructions, troubleshooting and a downloadable README.
The application runtime and evidence readers are bundled. AI features are optional and require a separate local model setup.
01
Install and launch
On Windows x64, run the MSI installer and launch Forensic Evidence from the Start menu, or extract the complete portable ZIP. On macOS, extract the archive, move the included .app to Applications and launch it. On Linux, extract the archive and run ./ForensicEvidence.Desktop. Keep archive contents together.
02
Open your evidence
Choose an evidence file or extracted folder. Create a case folder to save evidence references, item bookmarks and your workspace. Save the case before closing.
03
Add local AI when you need it
Install Ollama separately with nomic-embed-text for embeddings, gemma4:12b for AI queries, and qwen3-vl:2b-instruct for picture descriptions. In a case, open AI search, choose Process evidence, then enter your query. Model downloads are not included.
AI descriptions and matches can contain errors. Review the original evidence; results are a shortlist, not an exhaustive search or a forensic conclusion.
06 / QUESTIONS
Frequently asked. Answered plainly.
Common questions about the viewer, its platforms, and how it treats your evidence. For anything else, contact BBSoft.
01
Is Forensic Evidence Viewer really free?
Yes. Forensic Evidence Viewer is free to download and use on Windows, Linux and macOS. Version 0.3.17 packages for Windows x64, Linux x64 and macOS Apple Silicon are published with SHA-256 checksums so you can verify each download.
02
Which platforms does it support?
Version 0.3.17 supports Windows 10 or later (x64), Ubuntu 22.04 or compatible Linux (x64, glibc 2.35+), and macOS 14 or later on Apple Silicon. A legacy Windows ARM64 0.3.6 download remains available; it requires Windows 11 with x64 subprocess emulation and has not been runtime-tested on ARM64 hardware. Intel Macs are not supported.
03
Does it modify the evidence?
Evidence containers are opened read-only. Physical-disk acquisition opens the source read-only; logical mobile acquisition communicates with the device, and installing the optional Android collector changes device state. Opening a live folder can update operating-system timestamps, so examine copies or mounted images and use a write blocker where appropriate.
04
What evidence formats can it open?
E01, Ex01, L01, Lx01, AFF4, raw images, uncompressed LiME memory images, VMDK, DMG, PST/OST, Exchange 2013+ EDB, iPhone backups and Android collections, plus extracted folders. Read-only filesystem support includes exFAT, experimental APFS v2 and single-device Btrfs. NTFS deleted-file scanning can recover supported surviving MFT records; recovered content requires review. APFS unlocking, snapshots and Fusion drives, multi-device Btrfs RAID, and fragmented carving are not supported. Basic contiguous JPEG/PNG carving is disabled by default.
05
Does the AI search need an internet connection?
No. AI search is optional and runs through your local Ollama installation. Processing and the search index stay on your machine, stored in the case’s SQLite database.
06
What do I need for mobile acquisition?
iPhone USB backup acquisition requires Windows and installed Apple device drivers/services; the Apple Devices window does not need to remain open. Android USB collection requires separately installed Android SDK Platform-Tools, USB debugging and device approval. The optional collector requires Android 8 or newer, explicit permissions and a user-started export. It collects provider-exposed messages; complete RCS history and private app data are not guaranteed. If a development collector is installed, uninstall it before installing the release collector; computer-side collections remain available.
07
Can I acquire evidence from a remote computer?
Yes. From the desktop, open Acquire → Manage remote endpoints to generate an agent package for a supported Windows, Linux or macOS computer. Install and enroll the agent, then browse its permitted files and folders, select what you need, and collect it to your investigator computer over an authenticated, encrypted connection.
File and folder collections create a verified Lx01 logical image with hashes, signed receipts and acquisition records. Physical-disk acquisition and memory capture require separate permissions and selection. Memory capture supports Windows and Linux x64 endpoints; Linux packages include AVML and require root privileges and a kernel that permits acquisition. Available sources depend on the endpoint and its permissions; macOS file collection remains experimental.
08
Does Registry analysis use the investigator computer's Registry?
Registry analysis parses raw hive files from the selected evidence image or extracted evidence folder. It scans standard Registry locations by default, with an optional Search all folders mode. USB history, UserAssist, deleted-cell recovery and transaction-log replay are derived from those evidence files; the scan does not substitute the investigator computer's live Registry.
09
What can event log analysis tell me?
The Event Logs tab reads EVTX files from the evidence and summarizes supported recorded activity, including logons, remote access, account and service changes, scheduled tasks, PowerShell and Microsoft Defender. Open supporting events to review the underlying records. Available summaries and session links depend on the logs and auditing present; Sysmon summaries require Sysmon events in the evidence. Uncertain partial logon histories remain hidden.